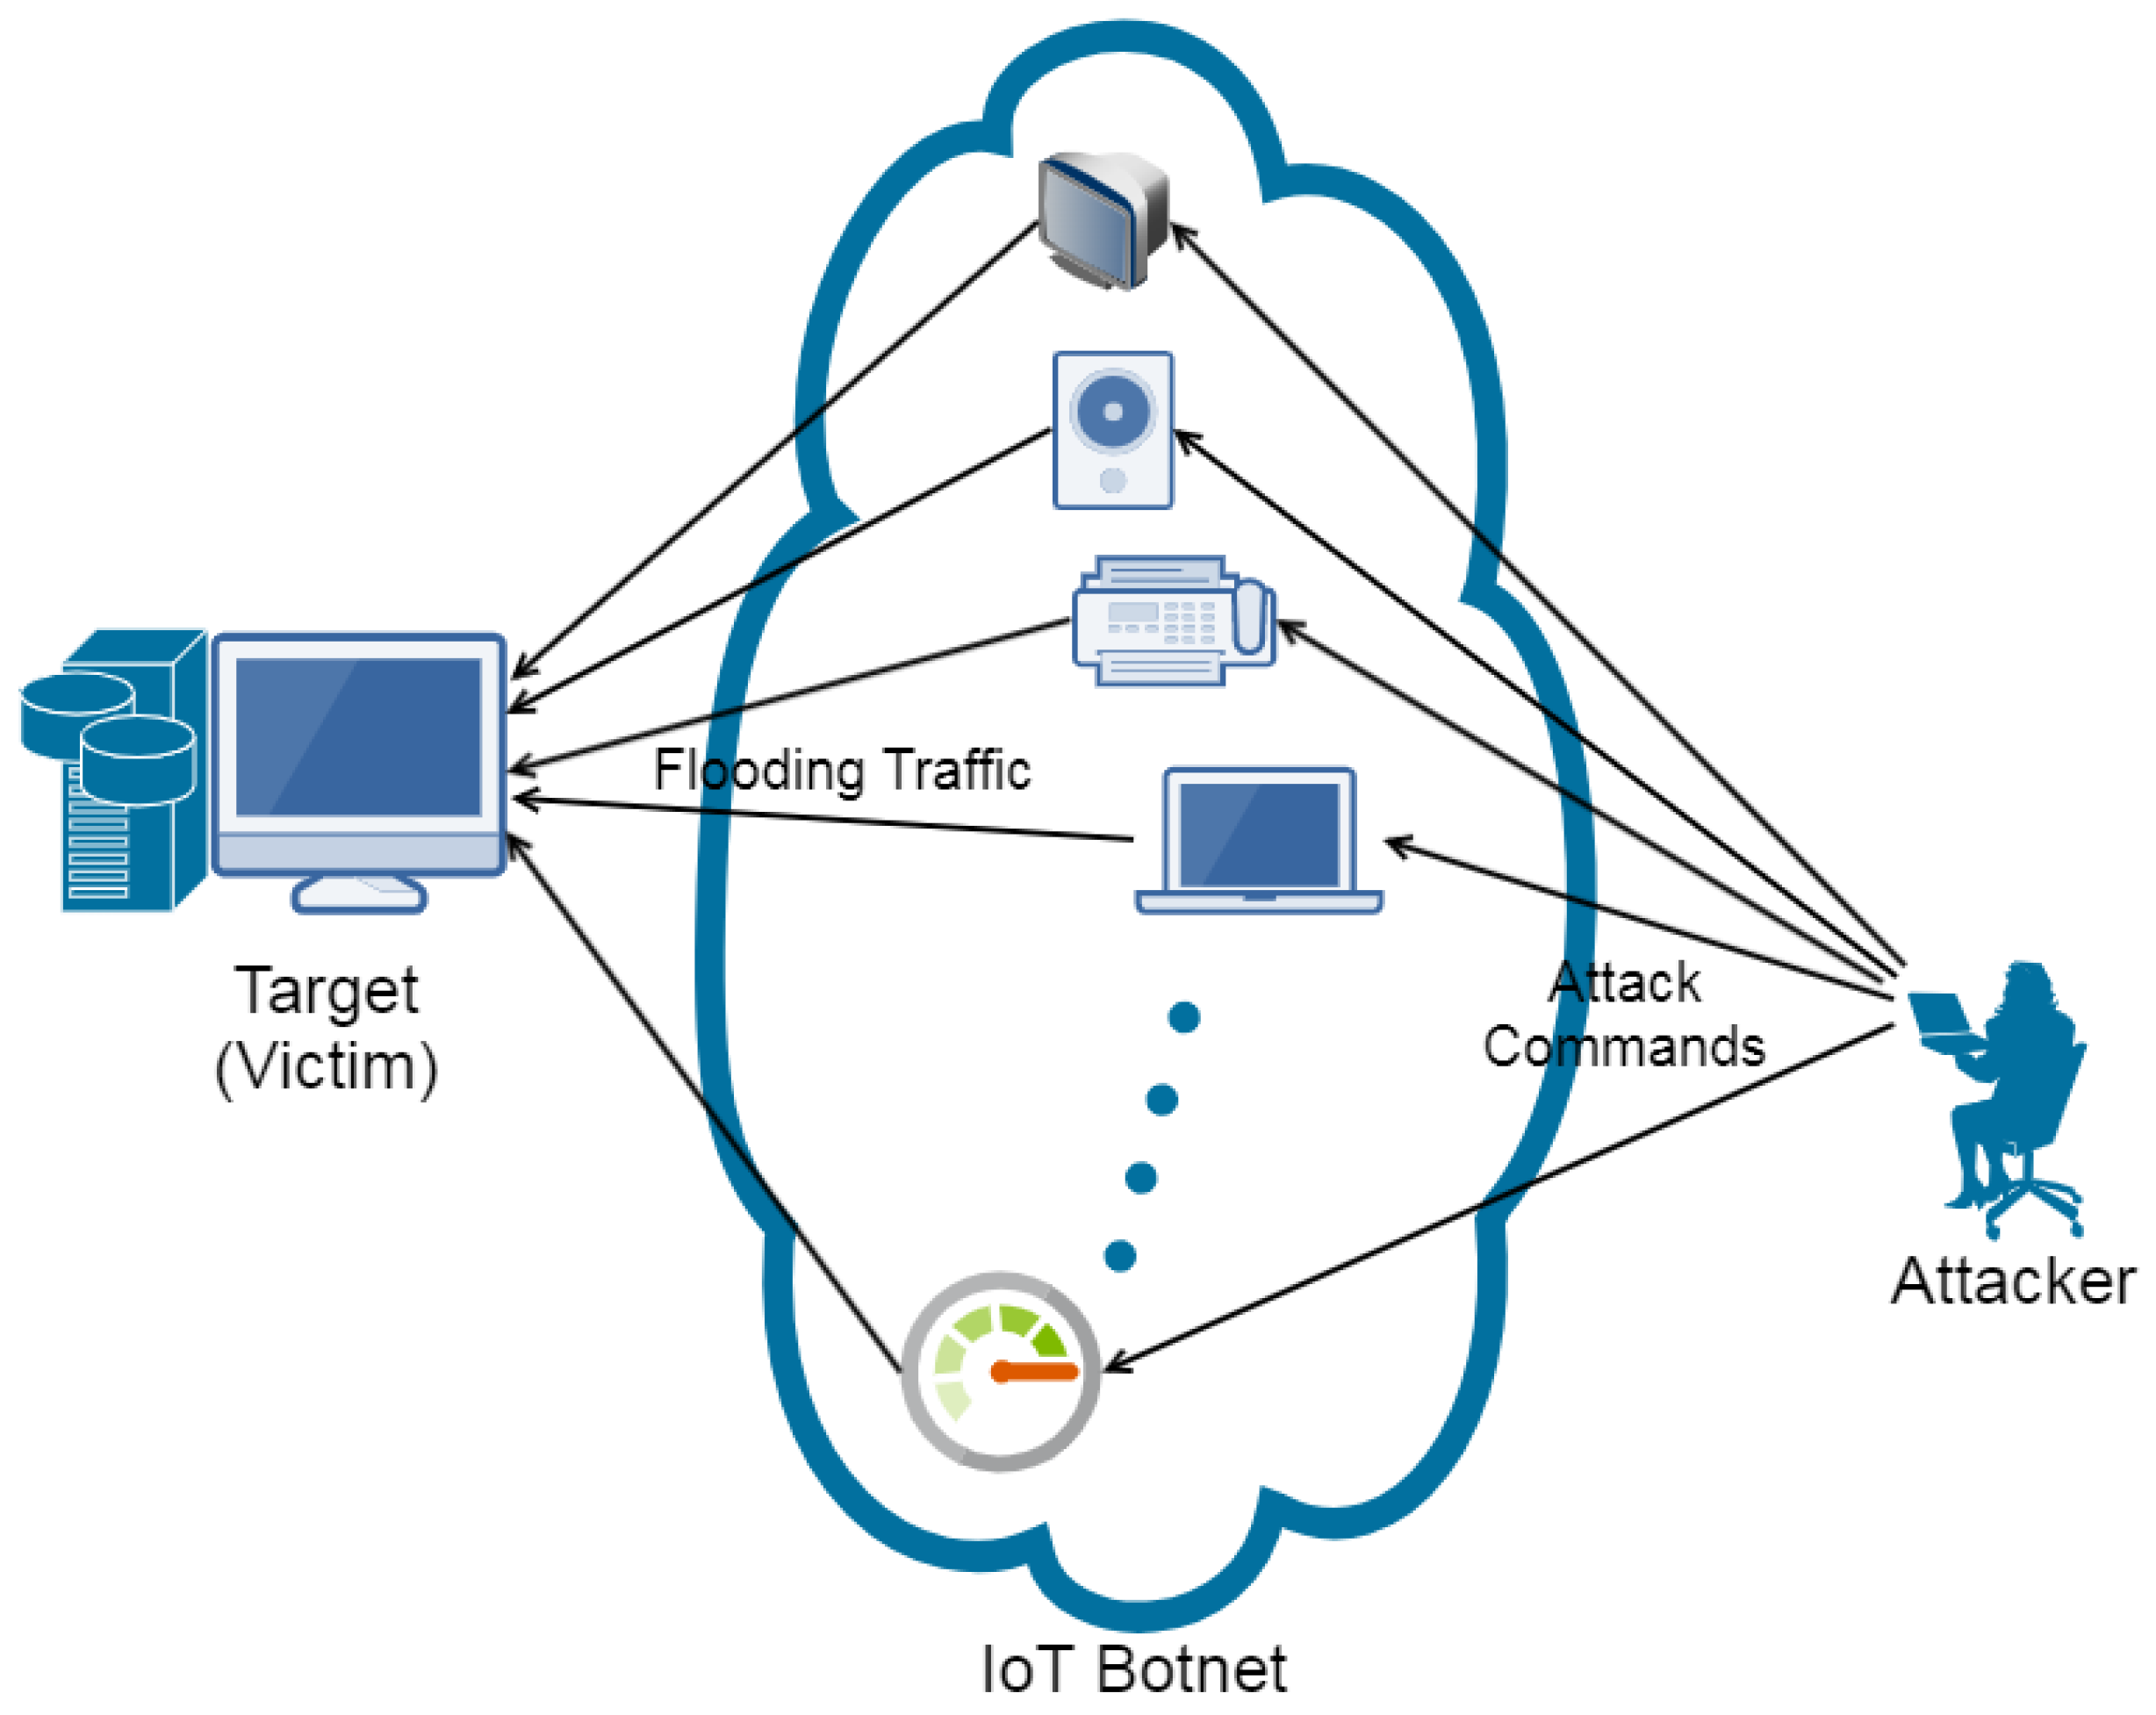
Netrouting differentiates itself by way of superior capabilities that enhance accuracy, scalability, and effectivity in handling sophisticated DDoS assaults while maintaining efficiency for respectable users. DDoS assaults usually rely on botnets and compromised devices spread throughout a global community, making attribution troublesome. Techniques like IP spoofing and DNS amplification further obscure origins, particularly when attackers exploit susceptible DNS servers. A community visitors identification system may be based on heuristics or fashions (e.g. statistical models) to be able to identify https://www.testking.us/evaluating-resource-risks-in-global-geothermal-infrastructure-projects/ reliable or malicious network visitors.
Bot Mitigation
Analyse live traffic to detect volumetric and packet-rate–based DDoS attacks in close to real time using configurable thresholds and detection logic. Advanced inspection tools analyze encrypted visitors to detect hidden threats, ensuring that attackers cannot exploit SSL/TLS channels to bypass safety options. Sensible filtering uses behavioral analysis and intelligent automation to differentiate between reliable and malicious visitors, lowering disruptions to customers and enhancing overall protection. DDoS safety are available a quantity of deployment fashions, each designed to deal with totally different business wants, threat ranges, and infrastructure environments. Choosing the right sort is dependent upon elements such as site visitors quantity, utility structure, and required degree of control.
✅ Absolutely autonomous mitigation – Throughout attacks, no user intervention is required, and no further subscriptions are needed. ✅ Sturdy structure – High-performance hardware seamlessly mixed with cloud-based scrubbing. That’s why ramping up your defences towards DDoS and lowering vulnerabilities can sometimes imply that small and comparatively simple design changes are required.

Radware Defensepro
Examples include UDP floods, which ship faux Consumer Datagram Protocol (UDP) packets to a goal host’s ports. The host’s resources are tied up in a useless effort to search out an utility to obtain these fake packets. ICMP floods, additionally called “ping flood attacks,” bombard targets with ICMP echo requests from a quantity of spoofed IP addresses. Right Now’s DDoS assaults are dynamic, use a number of vectors, and leverage evolving AI methods to evade your current DDoS defenses.
- In addition to the preliminary disaster that the DDoS assault creates, there are subsequent prices to deliver methods again on line and to re-build the part of the community that was affected by the DDoS attack.
- It can verify human interactions, control resource utilization, and improve holistic application safety.
- Downtime results in a direct loss of sales and enterprise opportunities as prospects are unable to access the companies.
A current examine reported that DDoS attacks towards critical infrastructure have increased by 55% within the final four years. Organizations can set up hardware- or software-based load balancers to course of traffic. They also can use anycast networking, which enables a single IP address to be assigned to several servers or nodes throughout multiple places so that traffic may be shared throughout these servers. As visitors will increase, the load is spread out, that means that the servers are much less apt to be overwhelmed.
Distributed Denial of Service (DDoS) assaults are a critical risk to businesses and organisations of all sizes. These attacks involve flooding a target with so much traffic that it turns into unavailable to respectable users. DDoS attacks can be used for a wide selection of functions, together with financial acquire, political disruption, or simply to trigger chaos.
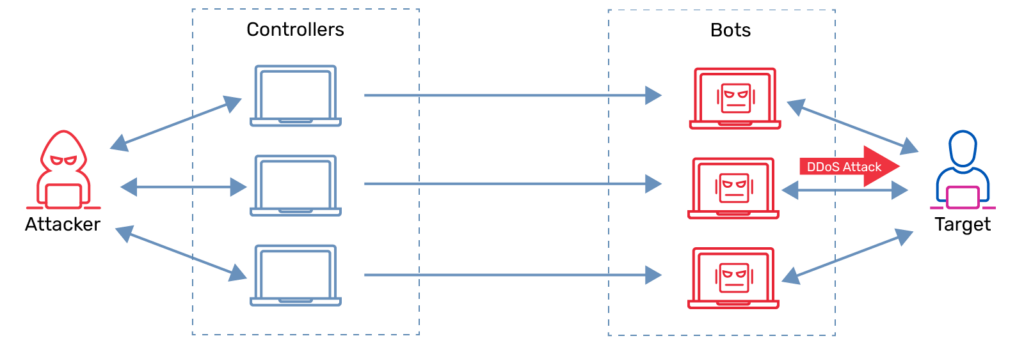
Challenges In Tracing Attack Sources
Entry plans start at $115/month, scaling to satisfy enterprise and ISP requirements. Pentanet deploys FastNetMon for real-time DDoS detection and automatic RTBH mitigation on the community edge. Conventional firewalls can’t totally deal with volumetric floods or massive scale DDoS site visitors.
AMX-IS runs FastNetMon as detection engine in its management community to detect and mitigate DDoS assaults. FastNetMon detects assaults and automatically diverts affected traffic to scrubbing centres utilizing routing-based controls. Engineers outline when diversion occurs and which prefixes are redirected, enabling seamless integration with on-premises or third-party scrubbing infrastructure. Apply dynamic IP blocklists from exterior menace https://www.twm-kd.com/improve-your-email-delivery-rates/ intelligence feeds or internal sources, enforced automatically at the community level as part of a layered DDoS defence. Apply targeted traffic filtering utilizing BGP FlowSpec to mitigate DDoS attacks with minimal influence on respectable site visitors. DDoS attacks symbolize a big and rising risk to fashionable businesses.
Selecting the proper resolution entails evaluating key concerns similar to scalability, cost, and deployment mannequin. Companies should select options that align with their operational needs and danger tolerance. A thorough evaluation identifies vulnerabilities in your community infrastructure and evaluates publicity to DDoS site visitors. If the mitigation is delegated to a special community, the provider’s decryption and re-encryption course of should meet your organization’s objectives by way of service and security.
The DDoS assault mitigation resolution ought to ideally be ready to use past data and predict website conduct. The quick need to get purposes again on-line includes important expenditure on technical resources, together with personnel, software, and hardware. Cybercriminals are gaining the sting in techniques to deny the service via DDoS attacks. These assaults can take your corporation offline for minutes, hours, and even weeks leading to substantial monetary and reputational injury. Implementing a DDoS mitigation resolution is essential to guard your business. Adaptive coverage engine minimizes injury utilizing machine learning for zero-day attack responses and accurate threat validation.